How to Protect the Digital Achilles Heel of Military Capability
Tom Burton


Subscribe Contact us

Our demographics and the moral value that we place on life as a society mean that our military must rely on technology to an ever increasing degree in order to exploit its advantages. However, the increased dependence on support from suppliers transforms the supply chain into an extended part of the networked battlespace, and thus its security and resilience has become a critical concern.


Capabilities with a Competitive Advantage also Bring New Vulnerabilities


In general, any new capability that has given our military a competitive edge also brings with it new vulnerabilities. A recent example is the introduction of GPS and other navigation systems. When these became widespread in the 90s, the risk of getting ‘geographically embarrassed’ was reduced, and thus members of the army bought consumer GPS receivers for personal use on exercise and operations. Thus, this capability represented a significant advance, and the joke that ‘the most dangerous thing in the combat zone is an officer with a map’ became less relevant. 


However, skills like map reading need to be learned and practised, and as such the more we rely on technological aids, the more we atrophy muscle memory. How many of us follow phone directions, only to realise we haven’t learned the route and have no feel for the environment we have just travelled through?


This effect is organisational as well as individual. The strive for achieving efficiency through digital transformation has led to fragility, with the loss of capacity and capability when digital services are disrupted. The global IT failure caused by CrowdStrike overnight on the 18-19th July demonstrates this clearly; in just a few hours, a software update crashed 8.5m computers globally, severely disrupting banks, airlines, rail services, healthcare, and other critical services. 


Maintaining full capacity in a reversionary mode is not economically viable once core business processes have been digitally optimised. However, reducing the likelihood and impact of a systemic incident like this requires systems to be designed with resilience from the outset.


Good Cyber and Data Security is about Much More than Preventing Data Leaks


It is natural to assume that maintaining data security is primarily about preventing someone from stealing confidential information. Granted, this has been an important consideration since spies first operated; this is why we classify and compartmentalise information.


However, confidentiality is only a part of the problem. If we look back at the trends over the last decade, many of the most damaging attacks have been ransomware. In these incidents, the attackers deny their victims the ability to access their own information until they pay a fee.


It is also vital to ensure that information is not modified covertly. It is an intriguing aspect of human nature that people frequently assume the information presented on a computer is completely accurate, when they would not have the same trust in information provided by a human. 


When serving, I saw staff officers assume that a unit’s location displayed on a digital map was accurate to within metres and always up to date. They knew, though, that the underlying information had been reported by a human to another human, over the radio, sporadically, and as an approximate six-figure grid reference. That instinctive belief in digital accuracy contrasts with the physical map table, where the information was recognised as inherently vague and out of date.


Protecting the availability of information and preventing its modification is just as important as preventing it from falling into the wrong hands.


Why do we need to care? What is the threat?


What must we protect to preserve our fighting power and freedom of manoeuvre on military operations? How could malicious actors undermine military capability? We first need to step above the world of ‘bits and bytes’ and decide what maligned intents might target us. The following are just a few examples, but they illustrate that the systemic nature of our digital landscape makes the risks far more complex and nuanced than they first appear.


Espionage


Espionage is as old as human conflict. Two and a half thousand years ago, Sun Tzu wrote a whole chapter on the importance of espionage and the use of spies. It is practiced across all contexts from the grand strategic and political levels, down to the compromise of tactical communications and devices. Espionage is also rife across the defence industrial base to gain insight and intellectual property about future weapon systems so that they can be countered and copied. 


Capability Denial


Even with Mission Command to empower and delegate, any operation relies on the efficient flow of information and commands to exploit opportunities and achieve the desired effects. This makes Command and Control capabilities a ripe target. One hour before Russia launched its full-scale invasion, it attempted to disrupt Ukraine’s C2 capabilities by executing a cyber-attack on the communications company Viasat. Disruption of communications bearers is an obvious approach, but a widespread attack on networked computers would be more complicated to recover from. And, as we realise the vision of an ‘Internet of Military Things’, described recently by the UK Chief of General Staff, by networking all elements of battlefield equipment, digital denial could extend across those platforms, disrupting intelligence, logistics, mobility, and fires.


Subversion & Deception


Subversion and deception are already directed at our personal lives; phishing attacks, spoofed websites, fake news, trolls, and bots all attempt to manipulate the way we think and act. A notable case involved an AI-generated deep-fake of a company CFO on a video conference call, leading to criminals defrauding Arup, a UK Engineering firm, by HK$200m (US$25m). 


It may be a while before we see Microsoft Teams in the trenches, but reachback from formation headquarters to the home-base is nothing new. Are we prepared for remote support into theatre, provided by partners and suppliers, being used as a vector to conduct highly realistic live deception and socially engineered attacks like the one Arup experienced?


Degradation of the Moral Component


The moral component – the ability to get people to fight – is the pre-eminent of the three essential elements that make up fighting power according to the UK defence doctrine. Many things would influence it, but a sense of confidence in the security and wellbeing of a soldier’s family at home is a key one. What if the family at home couldn’t access money because the military payroll system had been attacked? How quickly would force motivation and cohesion on operations deteriorate?


What is Being Done, and What More Should We Do?


The UK government has recognised the threats and risks for some time, and it has done a lot to reduce them. Cyber security has been recognised as a fundamental part of national security for over a decade, with the Defence Industrial Sector identified as critical national infrastructure. The Ministry of Defence’s (MOD) recent shift in governance policy to demand that systems are Secure by Design, and that a programme’s Senior Responsible Officer takes ownership and responsibility for risk, is significant progress. 


However, threat and risks are not static. Foreign state hacks, both covert and overt, have risen with geopolitical instability. In the most recent National Cyber Security Centre’s annual review, they specifically described the intensity and pervasive nature of the cyber threat from Russia. Cyber-attacks against our information, digital services, and infrastructure, will be a core component of any hybrid war, not least because of their deniability. We can see this today with attacks that closely correlate with the Kremlin’s interests and motivations, such as the recent attack by Russian hackers on NHS partners in London.


Fragile networks are only as strong as their weakest link. For some time, the defence ‘network’ has spanned the wider defence enterprise, which extends deep into the supply chain. Our need to maintain technological advantage and agility means we will need to source innovation far beyond the traditional Defence OEMs, and we will need to get updates into theatre quickly and frequently. This makes the supplier of a digital ‘widget’ part of the operational network, even if they’re not connected to it. 

So, the extended network is expanding and becoming increasingly operationally critical, and the capabilities and motivations of the geopolitical threats we face are evolving. What was adequate five years ago is unlikely to be sufficient for the next five. There are many steps that can be taken to respond to this change, and the following three focus on resilience in the extended defence network: 


Threat Escalation Contingency Planning


All networks have non-critical capabilities that deliver softer benefits and efficiency. However, every piece of software, network segment, or service presents a part of the surface that can be attacked. When the threat escalates, we can reduce our attack service by pre-emptively switching off non-core services, and further segmenting critical capabilities, all at the expense of efficiency. There is evidence that Ukraine’s resilience in the face of Russian cyber-attacks in 2022 benefitted from this preparation. Preparing and testing these measures takes time and imposing it on suppliers will also have commercial consequences. 


Enhanced Continuous Supplier Assurance


Supplier assurance for cyber risk has been an element of MOD risk management for some time, albeit the tools to facilitate it have been limited since the Octavian Supplier Cyber Protection Service was retired without replacement in 2021. However, when the scope of the networks at risk increases and the threats evolve, we need to change our posture. This will affect the suppliers to focus on, the questions we ask, and the standards we expect. Assurance needs to be flexible and dynamic; threat changes may require targeted or widespread reviews at short notice, with commercial as well as practical implications.


Cyber Stress Testing


The Bank of England introduced its Critical National Infrastructure Banking Supervision and Evaluation Testing (CBEST) in 2014 to assure operational resilience in the UK financial sector. Implementing the Defence equivalent of CBEST would take some significant time and effort to deliver results. However, without this type of activity, there is insufficient objective evidence that risk and resilience are tolerable.


Conclusions


Our demographics and the moral value we place on life as a society mean our military’s ability to deter and, if necessary, defeat a belligerent nation-state, will rely on it exploiting technological advantage. The evolution of conflict in Ukraine also demonstrates that industries will need to be able to deliver digital enhancements to that technology rapidly into theatre to maintain an advantage. But this introduces vulnerabilities well beyond the boundaries of Government departments and their Tier 1 suppliers. If the enemy can exploit these vulnerabilities, the impact would be significantly greater than the equivalent several decades ago.


The increased dependence on agile reachback support from suppliers makes the supply chain an extended part of the networked battlespace, and their security and resilience are critical components of the risk calculus. A lot of progress has been made over the last ten years. But this period has also demonstrated that we should expect a cyber-capable adversarial state to do against us. To prevent and, if necessary, prosecute a war in the future, we need to not just maintain, but significantly enhance our management of risk in the defence supply chain.


To find out more about our Cyber Security services and security philosophy, check out our service page.


To contact Tom Burton and arrange a free consultation, use the form below or email Tom at tburton@cambridgemc.com.

Contact - Digital Achilles Heel

Subscribe to our Newsletter

Blog Subscribe

SHARE CONTENT
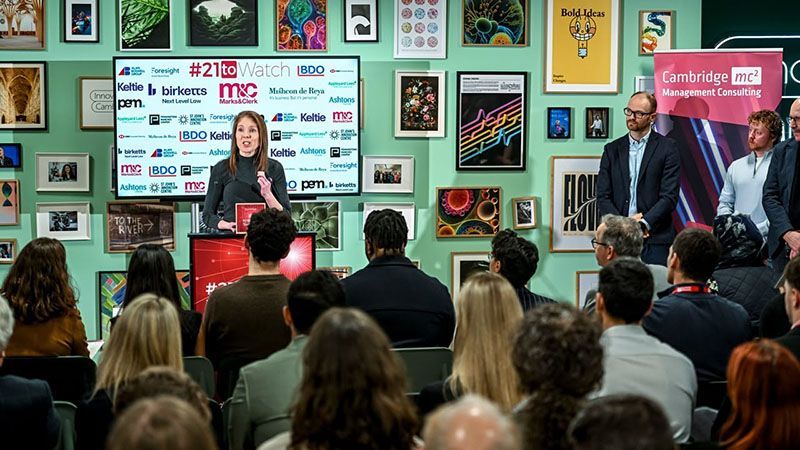
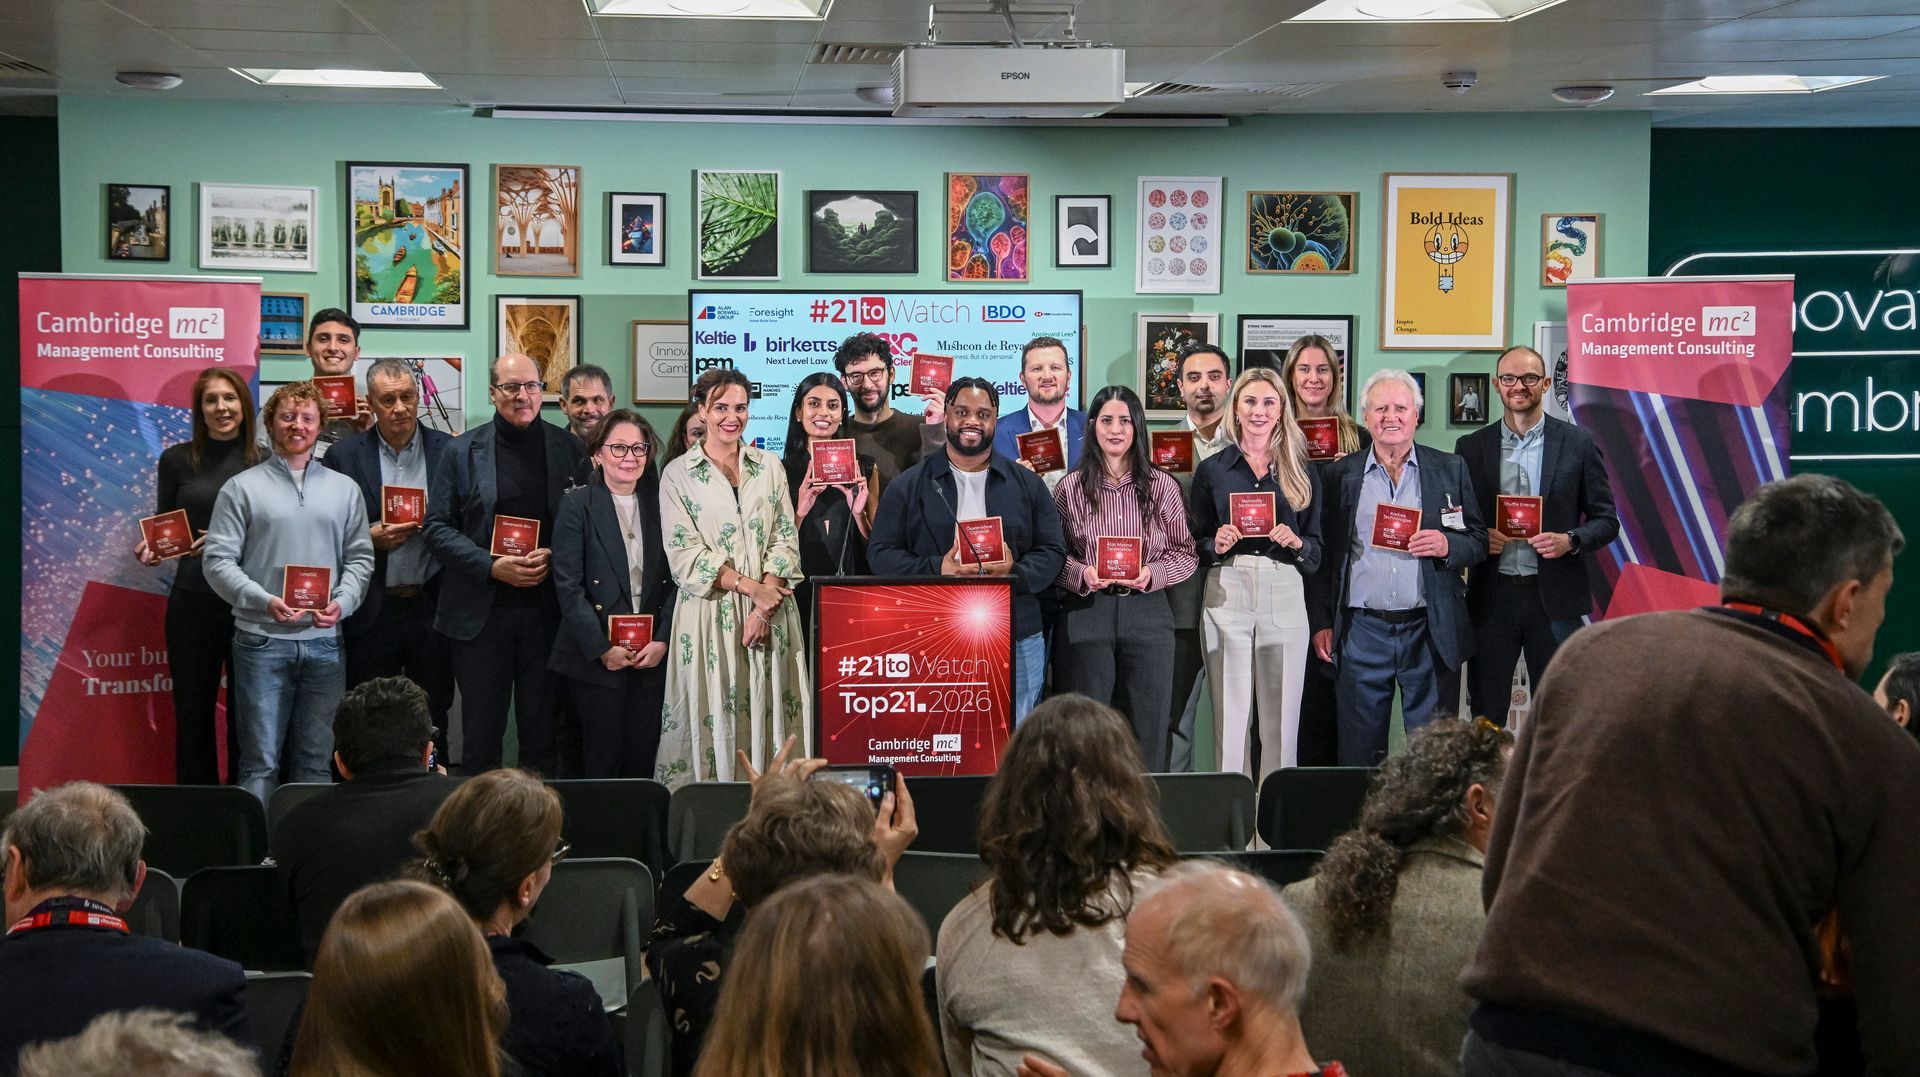
Photo of all the Top21 winners at the #21toWatch awards 2026, held at the Glasshouse in Cambridge.
by Jeremy Griggs • 18 November 2026
As #21toWatch 2027 opens, we look at how 147 winners from Cambridge’s innovation ecosystem have raised over £1bn and earned awards, fellowships, and more | READ FULL ARTICLE
Abstract technology image with the words 'Research Preview' overlaid.
by Charlotte Patrick • 17 November 2026
CAMBRIDGE AIQ | How can operators scale agentic AI towards autonomous networks? Our report sets out a five-stage roadmap, the key risks, and a framework for Stage 4 | READ PREVIEW & PURCHASE REPORT
16 November 2026
10 November 2026 – London – IThe search is on for the next generation of game-changing founders, pioneering companies and breakthrough innovations as #21toWatch opens the nominations window for its prestigious 2027 awards. Run by Cambridge Management Consulting, #21toWatch has a proven track record of spotlighting emerging talent and technologies from Cambridge and across the East of England - ventures with the potential to translate ambitious ideas into meaningful commercial and societal impact. Submissions typically span all areas of cutting-edge emerging innovation including artificial intelligence, deep tech, medtech, life sciences, biotechnology and climate technology. Some of the exciting entries already received for 2027 are as follows: In the ‘People’ category, biochemist, Dr Irina Gostimskaya, co-founder and CEO of Cambridge Molecular Computers, is a leading authority on reading, writing, and editing DNA. With her team at Cambridge Molecular Computers, she is building an alternative computing platform beyond silicon, using the programmability of DNA to solve previously intractable problems. Trading space for time, a DNA computer enables a desktop machine to outperform the world’s current fastest supercomputer, while consuming only a fraction of the energy. In the ‘Company’ category, pioneering femtech startup, Avline Health is building a pioneering intelligent clinical decision-support platform that combines individual patient risk assessment with evidence-informed treatment recommendations for genitourinary syndrome of menopause (GSM) after breast cancer. Combining vaginal microbiome sequencing, treatment history and longitudinal health data, Avline Health aims to provide clinicians with an objective severity score and a contraindication-aware treatment match, instead of a guess. CEO and co-founder, Dr. Josiane Chuisseu told us: “Vaginal microbiome testing does already exist - but nobody's built it for oncology before, and it’s very much needed. Up to 70% of breast cancer survivors develop genitourinary syndrome of menopause (GSM), a chronic and progressive condition caused by a drop in oestrogen levels - but it's chronically underdiagnosed because assessment still relies on subjective exams, and undertreated because clinicians are often too cautious to prescribe hormone therapy in cancer patients even when it's now shown to be safe. “As a result, two-thirds of women get the wrong diagnosis, and the treatments they do get are only effective less than 20% of the time." Meanwhile, in the ‘Things’ category, Metcycle is developing a scalable, energy-efficient technology to transform lithium-ion battery black mass into high-value critical materials. By addressing the industry’s key separation bottleneck, Metcycle aims to reduce reliance on energy-intensive and chemical-heavy recycling routes, enabling more economical recovery of battery metals while strengthening Europe’s domestic supply of critical raw materials. The 2027 #21toWatch campaign follows a year of incredible innovation across the region, with last year’s winning cohort continuing to make significant progress across investment, commercialisation and innovation: 2026 #21toWatch winner, Memorify has launched its Yoree memory platform following an oversubscribed £420k pre-seed investment round and a waitlist of more than 5,000 prospective users. Elsewhere, fellow winner, Loop52 has been selected for a share of a £2.7m Government-backed automotive innovation funding programme while another 2026 winner, Myonerv has won a £100k Innovate UK grant to advance clinical testing of its wearable stroke-rehabilitation technology, and 2026 winner, Cyclana Bio, which aims to find a cure for endometriosis, has secured approval for a 500-patient clinical study. Tim Passingham, founder and executive chairman of Cambridge Management Consulting, said: “Together, these achievements demonstrate the breadth of progress being made by the #21toWatch community, from attracting investment and bringing products to market to advancing clinical research and developing technologies with significant industrial potential. “#21toWatch is all about the importance of identifying promising innovators early and helping them gain the recognition and connections needed to scale. However, we are delighted that the impact of #21toWatch extends well beyond the awards.” Collectively, past winners have now raised more than £1billion, underlining the scale of the technical ambition among the ventures, and the importance of bringing such innovators to the attention of investors, customers and the wider business community. The #21toWatch shortlist – judged by a panel of independent judges - will be announced on 3 February 2027, with the final Top21, selected across three categories: People, Companies and Things, unveiled at an awards ceremony at Pembroke College, Cambridge, on 11 March 2027. Founders, companies and innovators can submit their own nominations through the #21toWatch website at https://www.21towatch.com/. Deadline for entries is 8 January 2027. Nominations are also invited from investors, universities and others across the innovation ecosystem. The judging process considers innovation, the challenge being addressed, influence, viability and memorability. Marks & Clerk returns as a premium sponsor of the 2027 #21toWatch campaign. Matthew Pinney, Office Managing Partner, Marks & Clerk Cambridge, said: “Cambridge has an extraordinary depth of entrepreneurial talent, and #21toWatch provides a valuable platform for recognising those innovators turning ambitious ideas into businesses with real commercial potential. We look forward to meeting this year’s cohort, learning more about their ambitions, and helping them protect and maximise the value of their innovations through intellectual property as they contribute to the region’s continuing success as a centre for innovation.” Further sponsors and the full judging panel will be announced shortly.
Big Ben and London cityscape at night – neon overlay
11 November 2026
Cambridge MC acquires Alpine Resourcing, a London-based public sector specialist, extending its reach across central and local government in the UK | READ PRESS RELEASE
A representation of agent boxes (prompts) linked into a workflow on a computer screen.
by Charlotte Patrick • 9 November 2026
RESEARCH & ANALYSIS | Cambridge AIQ assesses 13 vendors delivering agentic AI for service assurance, comparing four distinct strategies and the key factors operators must weigh | READ PREVIEW & PURCHASE REPORT
Audience at the recent launch event for the #21toWatch 2027 awards at the Glasshouse, Cambridge.
9 November 2026
A new monthly event series for scaleup founders, investors, and advisers at The Glasshouse, Cambridge. Starts 26 November with CMR Surgical’s Martin Frost CBE | READ FULL PRESS RELEASE
by Darren Sheppard • 5 November 2026
Procurement teams that invite structured external challenge — not resist it — build stronger, more defensible decisions. Learn how to use market testing and early supplier engagement to strengthen procurement authority, not undermine it | READ NOW
Visualisation of Earth with lines of data wrapped around it
by Eric Green • 4 November 2026
PROCUREMENT & AI | Neoscalers often buy the network last, under pressure. Eric Green explains the contract-term and cost risks, and how procurement discipline closes the gap | READ FULL ARTICLE NOW
30 October 2026
23 October 2026, Cambridge – Cambridge Management Consulting (Cambridge MC) has celebrated its annual corporate Green Day, bringing colleagues together for a day of environmental volunteering instead of a day in the office. On Friday 23 October, the international management consultancy, headquartered in Cambridge, teamed up with Cambridge City Council to improve wildlife habitat at Cherry Hinton Hall, a 12-hectare public park in south-east Cambridge. Working alongside the City Council’s Community Engagement team, the Cambridge MC team focused on the glade in the nature area at the rear of the park, cutting back grass, clearing away the cuttings, and sowing wildflower seeds. The work was designed to support the management of the green space and create better conditions for wildlife, while giving Cambridge MC colleagues a direct role in caring for their local environment. Tim Passingham, founder and executive chairman of Cambridge MC, explained: “Making a positive impact means being prepared to roll up our sleeves and contribute to the communities in which we work. Rather than treating environmental responsibility as an abstract corporate ambition, Green Day gives our colleagues the opportunity to contribute their time and effort to community green spaces – turning our commitment into something tangible by working alongside our local community, supporting the places we share and recognising that small, practical actions can make a difference when we take them together. “The initiative also reflects the importance of collaboration in environmental action. Individual volunteers, community groups, businesses, and local authorities all have an important role to play in maintaining accessible green spaces and supporting urban biodiversity.” While Cambridge was the focus of the company-wide initiative, Green Day extended beyond the city, with events taking place in the New Forest, and planned initiatives in London which were unfortunately cancelled due to adverse weather. In the New Forest, Cambridge MC colleagues worked with local environmental group ECO SWAY on preparing shared green spaces and planting pollinator-friendly bulbs to support bees and butterflies in the spring. Unfortunately, the London team’s efforts were cancelled due to Storm Austen, however they were excited to be joining local volunteers from Stoke Newington Urban Green (SNUG) to water and mulch young trees ahead of winter, helping them to establish and reach maturity. As an international consultancy, the team’s environmental efforts did not stop there. In France, one Managing Partner contributed to his local ecosystem by planting an oak tree, and in Portugal another Partner showed her support by planting several fruit trees. Elsewhere, consultants based outside of the UK or simply unable to travel to the three primary locations sowed tree bombs as a remote way of amplifying the day’s overall mission. Green Day forms part of Cambridge MC’s wider commitment to using its expertise, time, and resources to create positive impact. The purpose-beyond-profit company commits at least 10% of its profits to charitable causes that tally with its ‘Five Cs’: Children (and young people), Conservation (and sustainability), Cancer, Communications, and Cambridge (the Cambridge ecosystem). Alongside financial support, Cambridge MC also engages in purposeful pro bono work, gifting at least 1% of its time and expertise to help charities mature, digitalise, and reduce costs. And, uniquely, the company holds 1% of its equity in reserve for charitable use should an equity event occur. In September, Cambridge MC achieved Certified B Corporation status, marking a significant milestone in the company’s commitment to responsible business and recognising its approach to creating value for its team, clients, community, and the environment alongside commercial success. Tim said: “Our approach recognises that a responsible business is not defined solely by the advice it gives clients, but also by the contribution it makes to the communities and environments in which it operates. “By combining hands-on work with local partners across Cambridge and the New Forest, the Green Day initiative is bringing this principle to life – one green space at a time.”
More posts